The key facts
- The Russian Interior Ministry warned about fake Wi-Fi networks that intercept logins, passwords and payment details
- QR codes from unverified sources may lead to phishing and fake payment pages
- Through switched-on Bluetooth, fraudsters can gain access to contacts and messages
Warning about Wi-Fi 'clones'
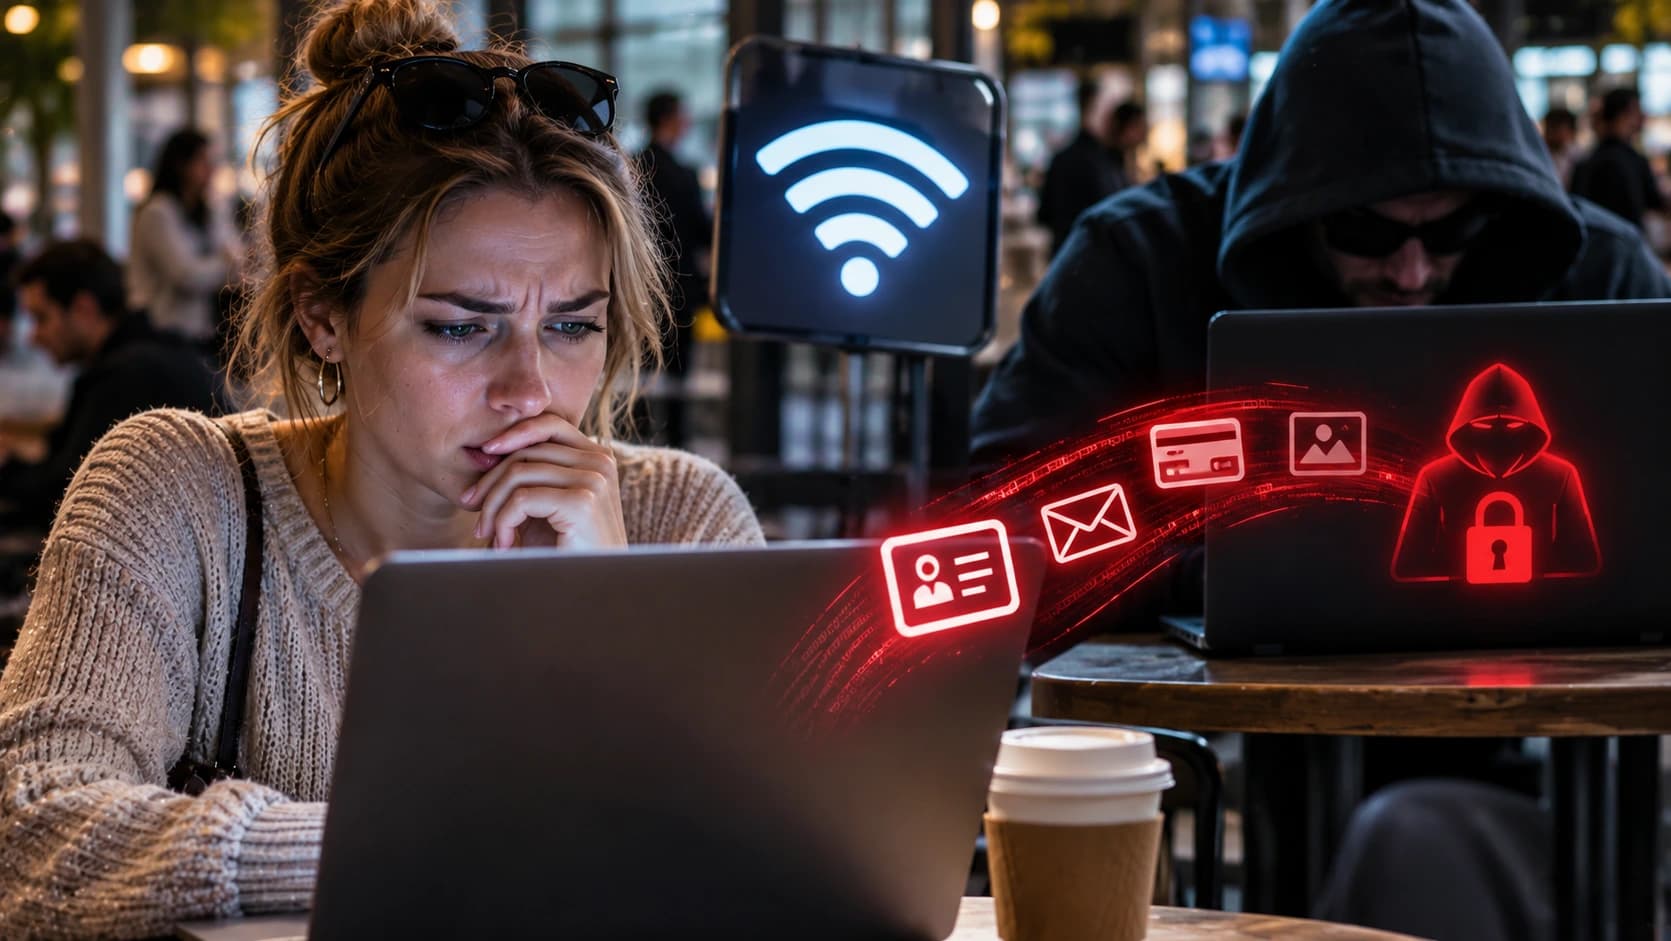
The Russian Interior Ministry's Directorate for Combating the Unlawful Use of Information and Communication Technologies has warned about the risks of using open Wi-Fi networks in public places, reports Gazeta.Ru citing RIA Novosti. According to the ministry, criminals create fake 'clone' networks to intercept users' logins, passwords and payment details.
Interior Ministry recommendations
The Interior Ministry recommended not entering personal information on public networks and checking the official name of the access point with venue staff. A separate warning concerns QR codes: they should not be scanned from unverified sources, as they may lead to phishing sites and fake payment pages. According to ministry representatives, Bluetooth left switched on also poses a danger — through it, fraudsters can gain access to contacts and messages, so unknown connections and files should not be accepted.