The key facts
- Hackers attacked the web server of Berlin's Charité hospital and stole personal data of employees, students, and people who had contacted the hospital
- The exact number of victims has not been disclosed; the hospital promised to personally notify everyone affected
- A week before the attack, the hospital's website was temporarily taken offline due to a PHP vulnerability, but the administration said the attack was not related to this
What happened
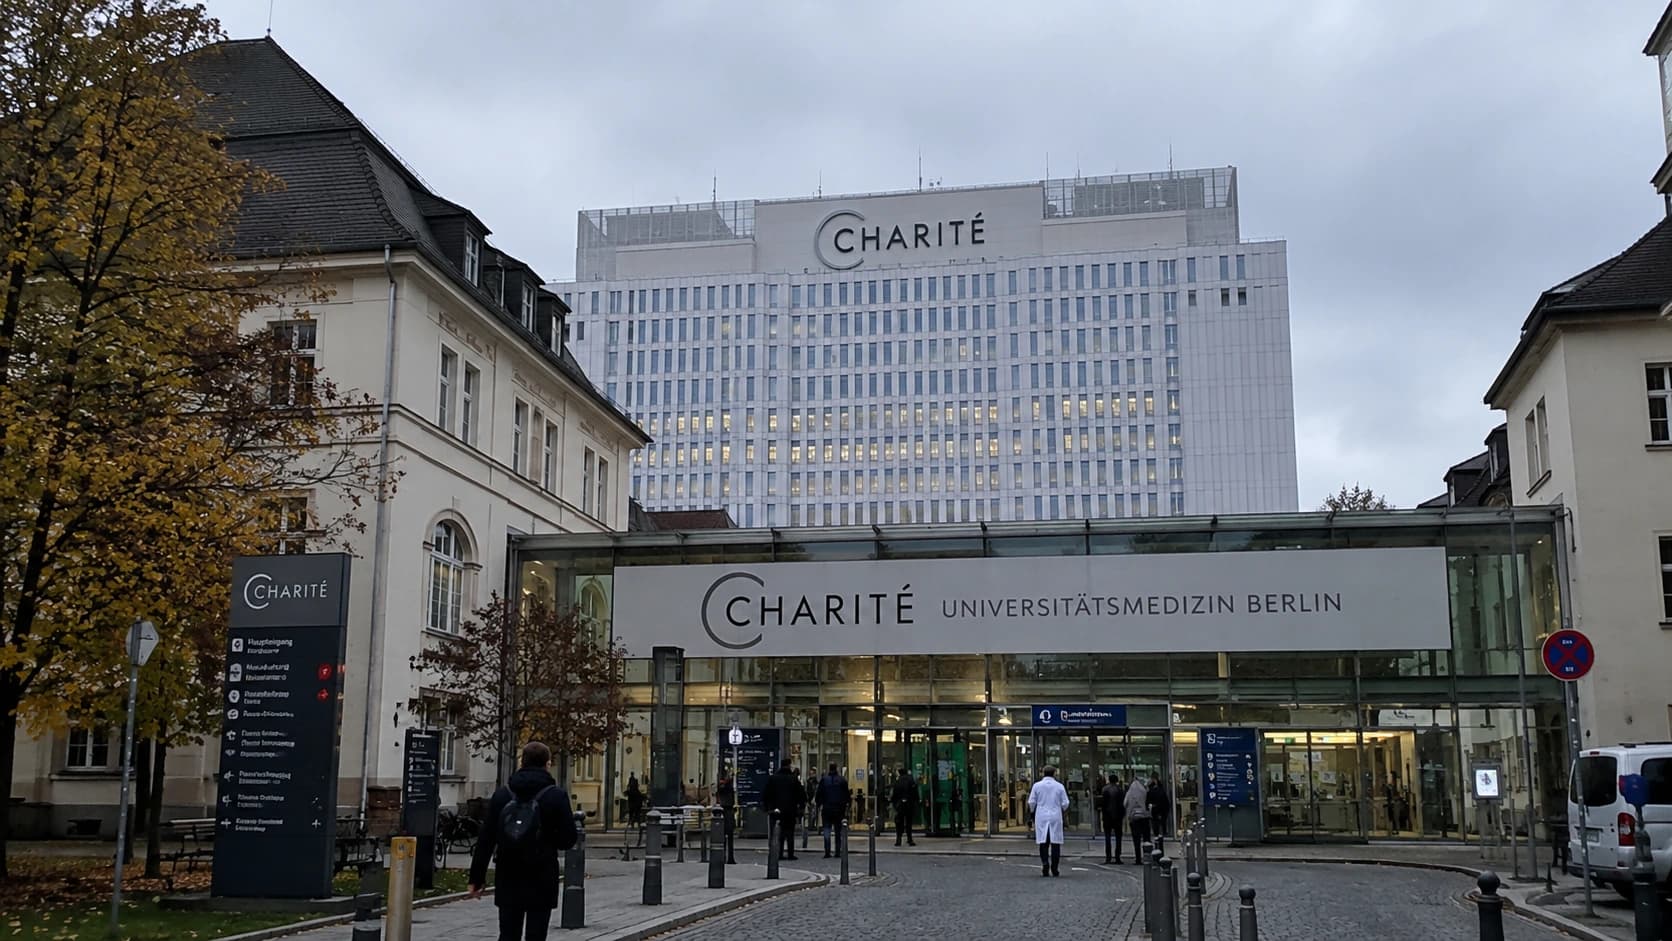
Hackers attacked the web server of the Berlin university hospital Charité — one of the largest in Europe — and stole personal data of employees, students, and people who had contacted the medical facility. This was reported on the hospital's official website. The leak affected contact information of users of online forms, including those who had tried to book a doctor's appointment. The exact number of victims has not yet been disclosed.
The hospital's response
Charité's administration promised to personally notify everyone whose information was compromised in the near future. After the attack was detected, specialists determined the cause of the incident and strengthened the security of other information systems; the management is also cooperating with supervisory and law enforcement agencies, which are investigating what happened. The hospital emphasized that medical care for patients was never interrupted, the hospital is operating normally, and prompt measures limited the consequences of the breach.
Connection with website shutdowns in Germany
A week before the attack, the hospital had temporarily taken its website offline due to a discovered vulnerability in PHP, but the administration assured that the current attack was not related to that issue. According to Life.ru, hospitals, universities, and government institutions in Germany had previously taken their websites offline en masse due to the threat of hacker attacksthe reason was two critical vulnerabilities in PHP that allowed access to servers and theft of data. Thus, the hospital is distancing this incident from the wave of shutdowns, although the coincidence in timing and the affected technology remains notable — an official explanation of the cause of the breach has not yet been published.