The key facts
- CISA confirmed exploitation of PHP vulnerabilities in real-world attacks and required US civilian federal agencies to install patches within three days
- The PHP2Shell bugs allow remote server compromise without a password; PHP is used on roughly 70% of web servers
- The vulnerabilities were found two years ago but deemed impractical; an exploitation method emerged after researchers at Calif worked with an AI model
The US government confirmed attacks on vulnerable PHP
The American cybersecurity agency CISA announced on Monday that hackers have begun actively exploiting a pair of critical vulnerabilities in the widely used web language PHP, and ordered civilian federal agencies to patch their systems within three days. In its statement, CISA did not name who is behind the attacks, but its warning came shortly after security researchers reported finding signs of the bugs being exploited in the wild.
What is known about the PHP2Shell vulnerabilities
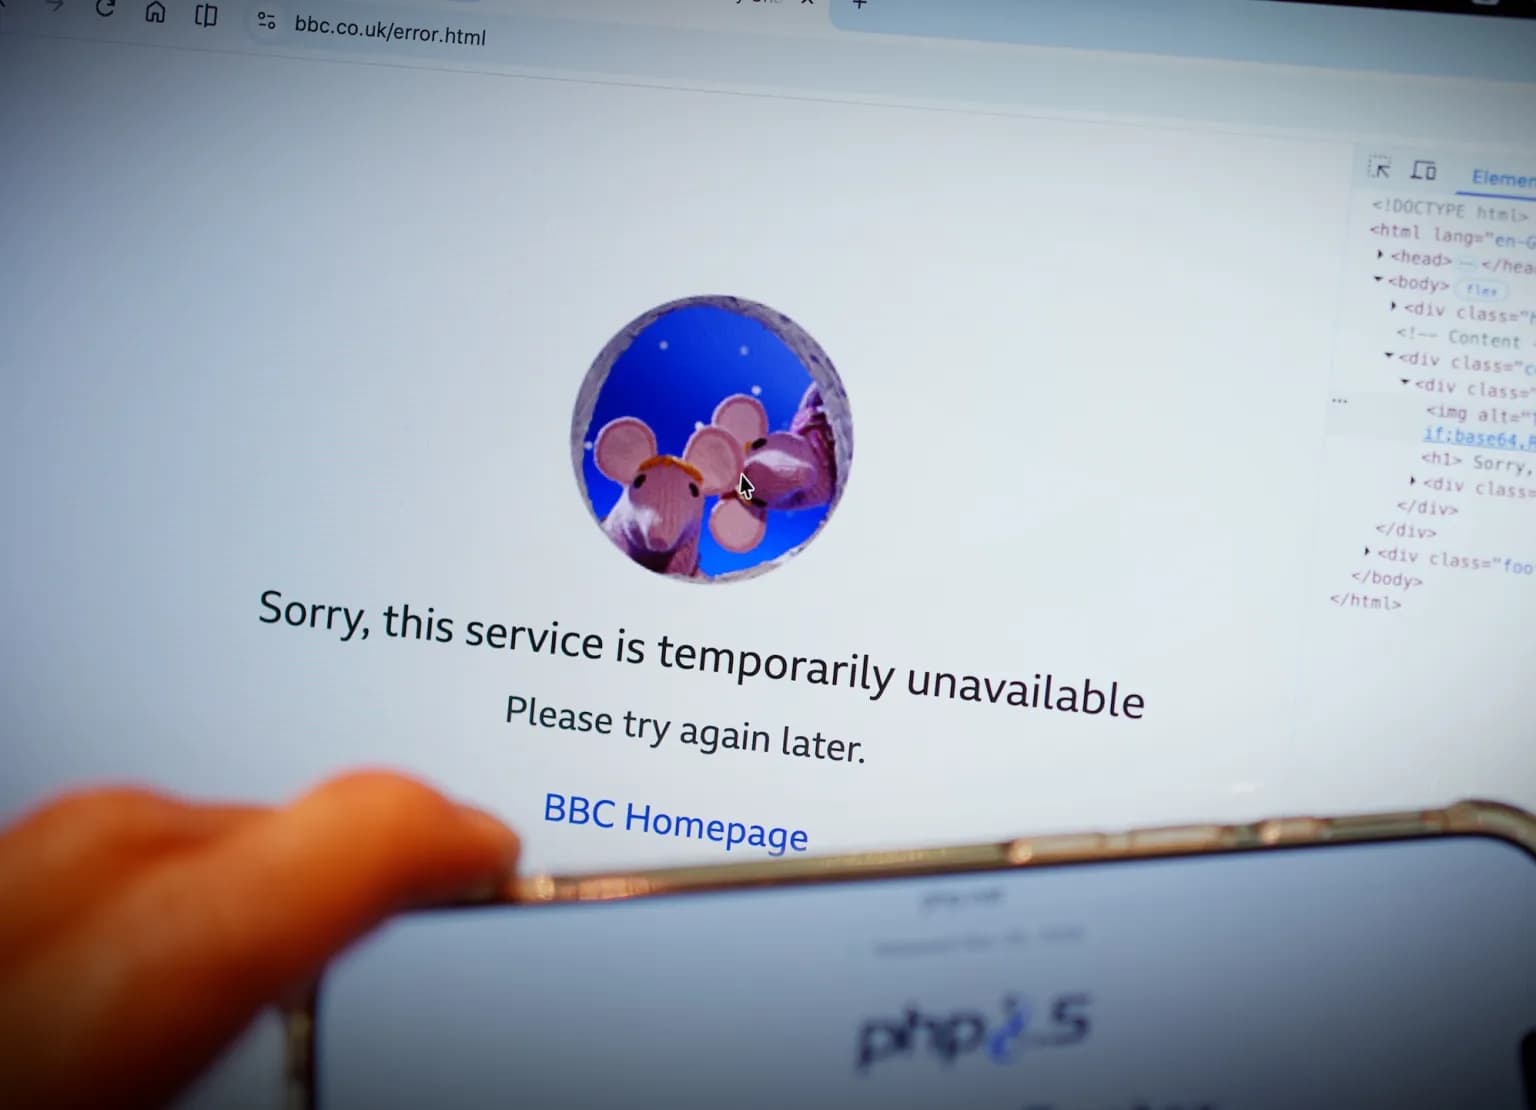
The vulnerabilities, dubbed PHP2Shell, allow attackers to remotely break into a vulnerable system over the internet without a password. According to available data, PHP is used on roughly 70% of web servers, so major websites and applications are at risk; the severity of the bugs has already prompted some governments and large companies to temporarily take their sites offline for patching. The language's developers released patches less than a week before the new CISA warning. At the same time, as researchers noted, building a working exploit was initially difficult, though possible — confirmed attacks in the wild now add pressure on organizations to update and avoid compromise and data leaks.
From 'impractical' bugs to real attacks: the role of AI and underfunding
The vulnerabilities went undetected for years: they were first found two years ago, but the nonprofit organization that maintains PHP said at the time that hackers had no practical way to exploit them, and the bugs were not fixed. The situation changed earlier this year, when researchers at the company Calif used an AI model to find a way to trigger both 'dormant' vulnerabilities. TechCrunch notes that these bugs are an example of vulnerabilities that went unaddressed for years but became relevant due to the growing ability of AI models to find and exploit security flaws, including chaining several flaws together. The publication also points to a systemic problem: PHP is one of many aging web technologies that have been underfunded for years, and open-source projects like PHP find it hard to pay for security audits that could catch such mistakes earlier.