The key facts
- Fraudsters are sending fake pre-trial claims for several million rubles with malicious attachments
- Attackers pose as employees of legal departments and analytical units without explaining the substance of the claim
- The MVD urges people not to open suspicious attachments and not to succumb to pressure
A new scheme involving fake claims
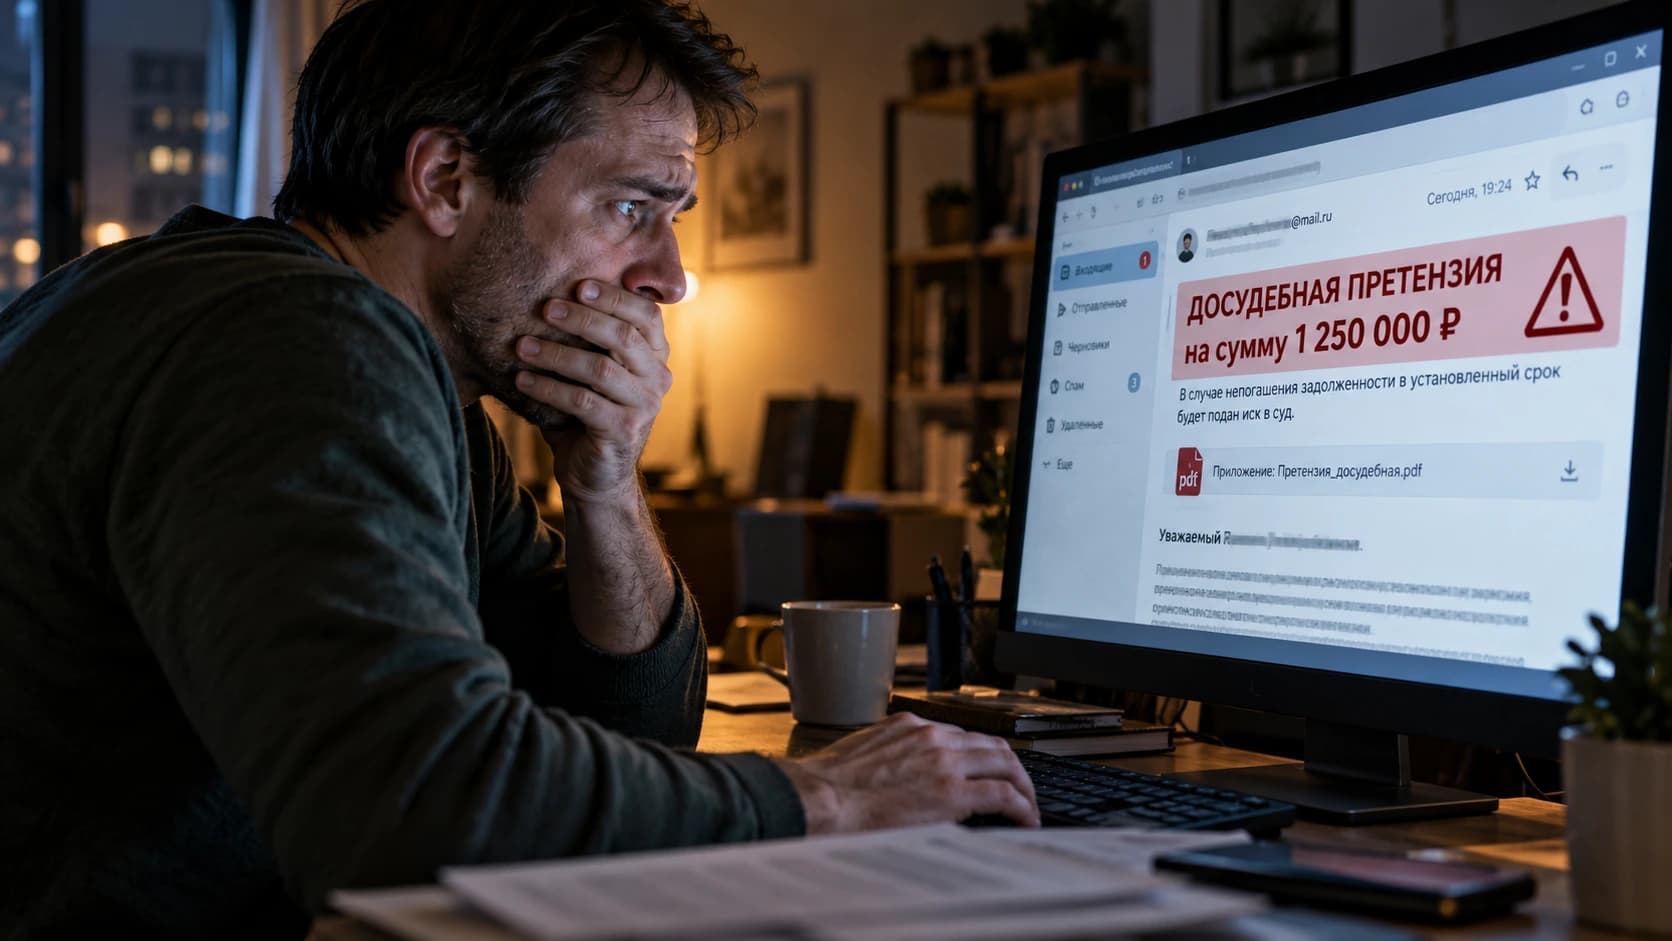
Fraudsters have begun sending Russians emails with fake pre-trial claims for several million rubles, TASS reports, citing materials from the Russian Ministry of Internal Affairs. Behind the threats of large recoveries are malicious files that the attackers use to try to gain access to devices and steal money or personal data.
How the scheme works
The scammers pose as employees of legal departments or analytical units and demand payment of an allegedly existing debt. At the same time, the messages do not explain what caused the claim or on what grounds the person faces a recovery. The criminals' main goal is to frighten the recipient with a multi-million sum and make them open an attached document that contains malicious software. After a computer or smartphone is infected, the attackers gain the ability to steal the user's personal information and attempt to take possession of their money.
MVD recommendations and similar schemes
The Ministry of Internal Affairs urged Russians not to succumb to pressure and not to open suspicious attachments in emails, especially in cases where the sender demands urgent action but does not explain the substance of the claims. Earlier, Life.ru reported on a related scheme: fraudsters sent out letters about non-existent tax debts with viruses in the attachments, posing as employees of government agencies, threatening forced recovery and penalties, and then offering to open an infected archive or follow a link to verify details. Experts at the time also urged people not to open suspicious files, even if the sender rushes or intimidates the recipient.
Why this matters
The scheme can affect virtually any email user: the pretext for the attack is the ordinary fear of court-ordered recovery, and infecting a device gives attackers access to money and personal data. The practical takeaway from the MVD materials is simple: letters about debts without an explanation of the grounds and with a demand to urgently open an attachment or follow a link should be ignored, without opening the files.